A serious flaw has been found in APT, the tool that installs software packages on Debian and Ubuntu (CVE-2026-109518). Ubuntu rates it high priority, and the APT developers call it critical. It was found by researcher Max Justicz.
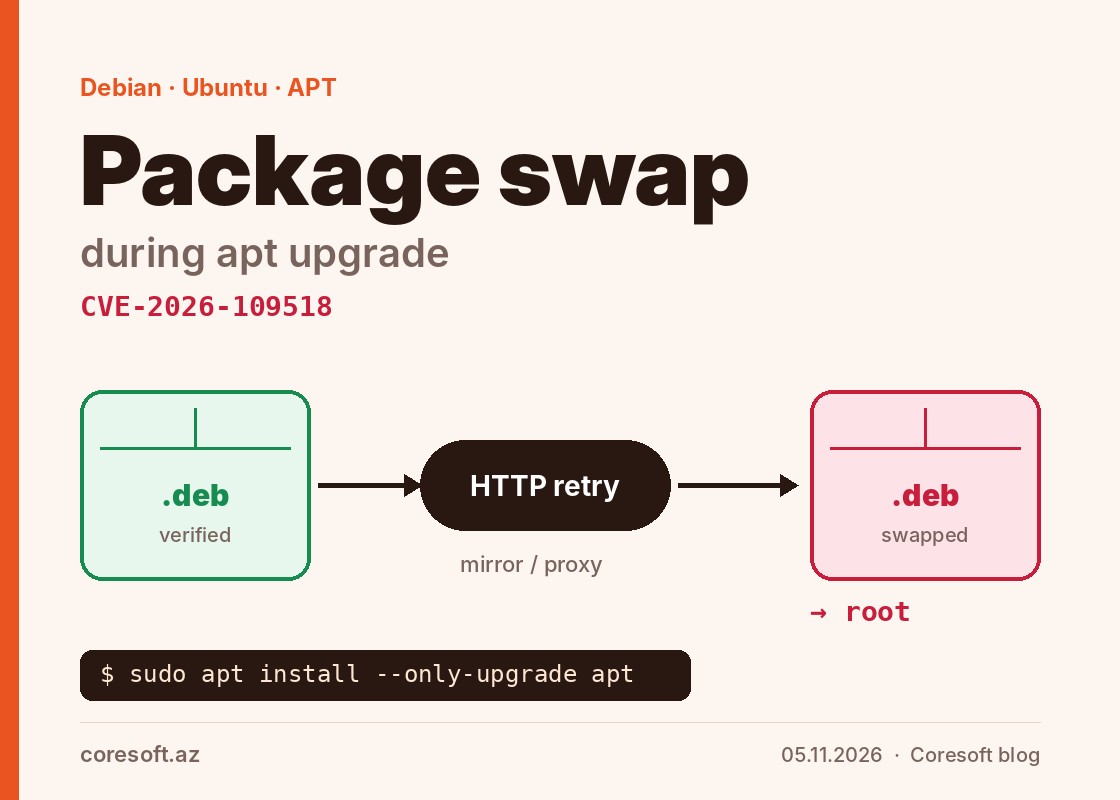
The problem lies in the retries APT makes when a download fails. An attacker who can modify the HTTP traffic between the server and the package source, for example through a malicious mirror or proxy, forces APT to retry the download and swaps the already verified package for their own file. When the package is installed, the attacker's code runs as root. In other words, the server can be taken over right while it is being updated.
Download retries are on by default from Debian 12 and Ubuntu 22.04 onward. On Debian 11 and Ubuntu 20.04 the setting is usually off, but if Acquire::Retries has been enabled in scripts, they are at risk too. There are no reports of the flaw being exploited in real attacks so far.
What to do
- Update APT itself:
sudo apt update && sudo apt install --only-upgrade apt. For example, the fixed version is 2.8.4ubuntu0.1 for Ubuntu 24.04 and 2.4.15ubuntu0.1 for 22.04. - Check your package sources: don't use unknown mirrors or proxies, and switch to HTTPS sources where you can.
- On older releases, check whether your scripts set
Acquire::Retries.
Here the update you run for security becomes the attack path itself. That is why where and over which channel your servers get their updates matters as much as the update itself.
Sources: The Hacker News, Ubuntu Security.