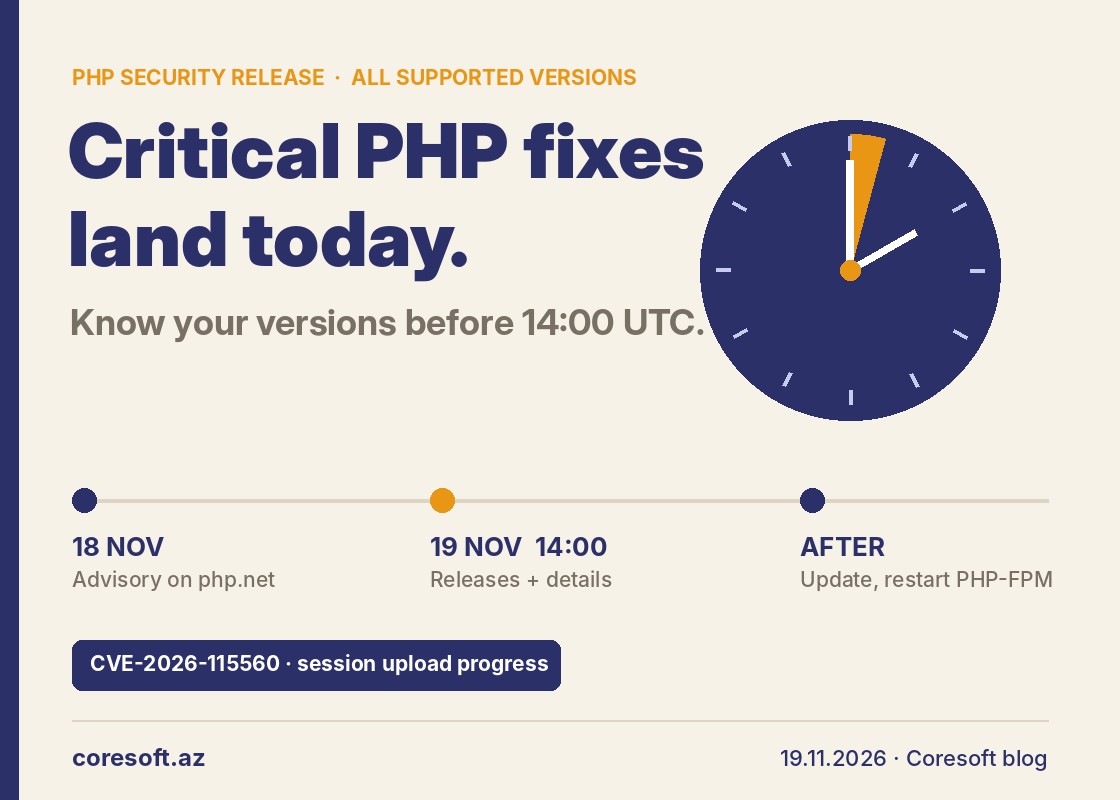
On 18 November the PHP team posted a notice on php.net: security releases for all supported PHP versions will ship on 19 November, between 14:00 and 14:30 UTC. The most serious of the fixed flaws is rated critical.
This is not an emergency release like October's PHP2Shell fix. It is PHP's regular release that comes out every four weeks. According to the team, the critical issues only trigger with non-default configuration or uncommon setups. Technical details and the fixed version numbers will be published together with the releases.
One of the expected fixes is already known: CVE-2026-115560, a remote code execution flaw in the feature that tracks file upload progress through the session. It needs a rare combination to work: session.serialize_handler must be set to php_binary or php_serialize, the code must switch it to php with ini_set() before the session starts, and upload progress must be enabled. In October PHP recommended session.upload_progress.enabled=0 as a temporary measure. If your site does not use this feature, you can turn it off now.
A low risk is no reason to put the update off. Check which PHP versions run on your servers now, and once the release is out, try it in a test environment first and then roll it out to production. If you use Linux distribution packages, follow your distribution's advisory. After updating, restart PHP-FPM or the web server so that old processes do not keep running.
We covered October's PHP2Shell flaws in an earlier post.
Sources: php.net, The Register, The Hacker News, Aikido