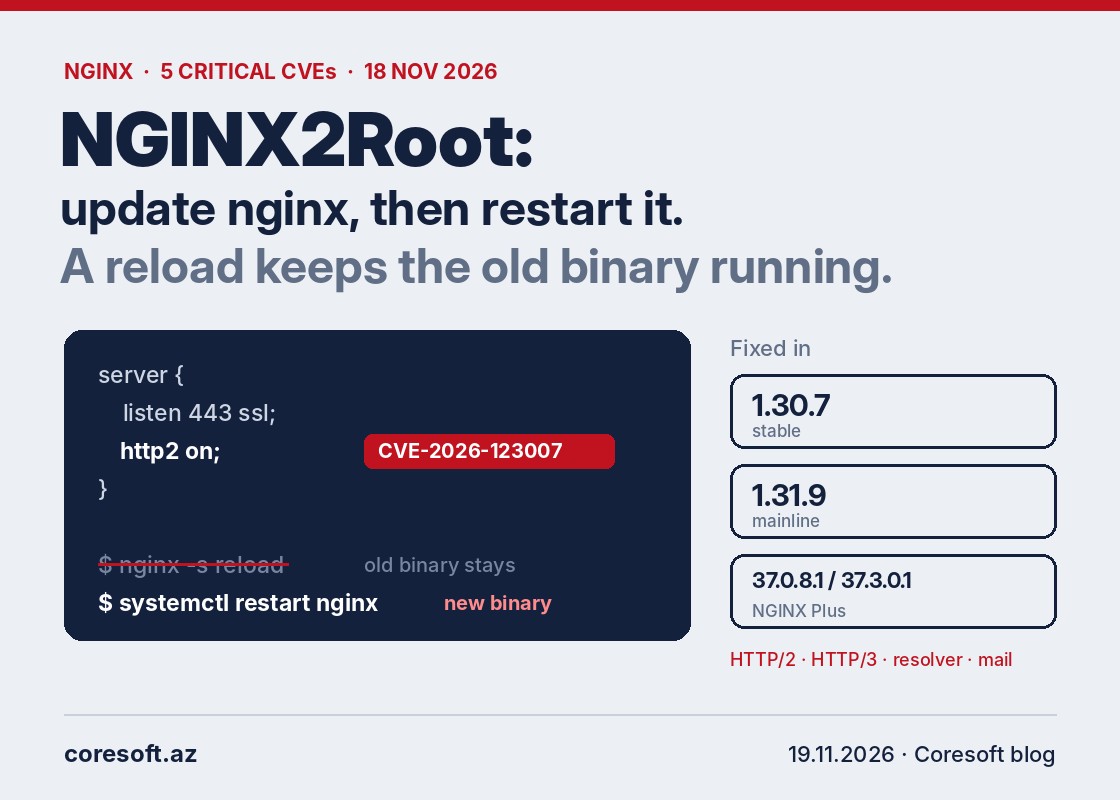
On 18 November F5 shipped an out-of-band security release for nginx. The stable 1.30.7 and mainline 1.31.9 versions fix ten flaws. Researchers grouped five of them under the name "NGINX2Root": under the right conditions they can lead to code execution on the server without any login.
The one getting most attention is CVE-2026-123007, an integer overflow in HTTP/2 flow control that has been in the code since 2015, nginx 1.9.5. All it needs is HTTP/2 over TLS, which is a routine setting on many sites. A public PoC already exists, but the attack is not easy: it has to defeat ASLR and push roughly 128 GB of HTTP/2 traffic. No attacks in the wild have been reported so far. The other flaws involve HTTP/3, the resolver and the mail proxy. For CVE-2026-118899, a denial of service over TLS 1.3, there is no workaround at all.
There is one step many people skip when updating. Upgrading the package and running nginx -s reload is not enough, because a reload keeps the old executable running. Restart the service fully with systemctl restart nginx. Linux distributions may backport the fixes under an older version number, so check the package version and your distribution's advisory rather than nginx -v. On Docker, pin the fixed image tag and recreate the containers.
If you cannot update right away, http2 off; temporarily closes the two HTTP/2 flaws, but not the rest. Also check the error log for worker crashes ending in "exited on signal": they can be a sign of exploitation attempts.
Sources: Tenable, CERT-EU, Atlas Security