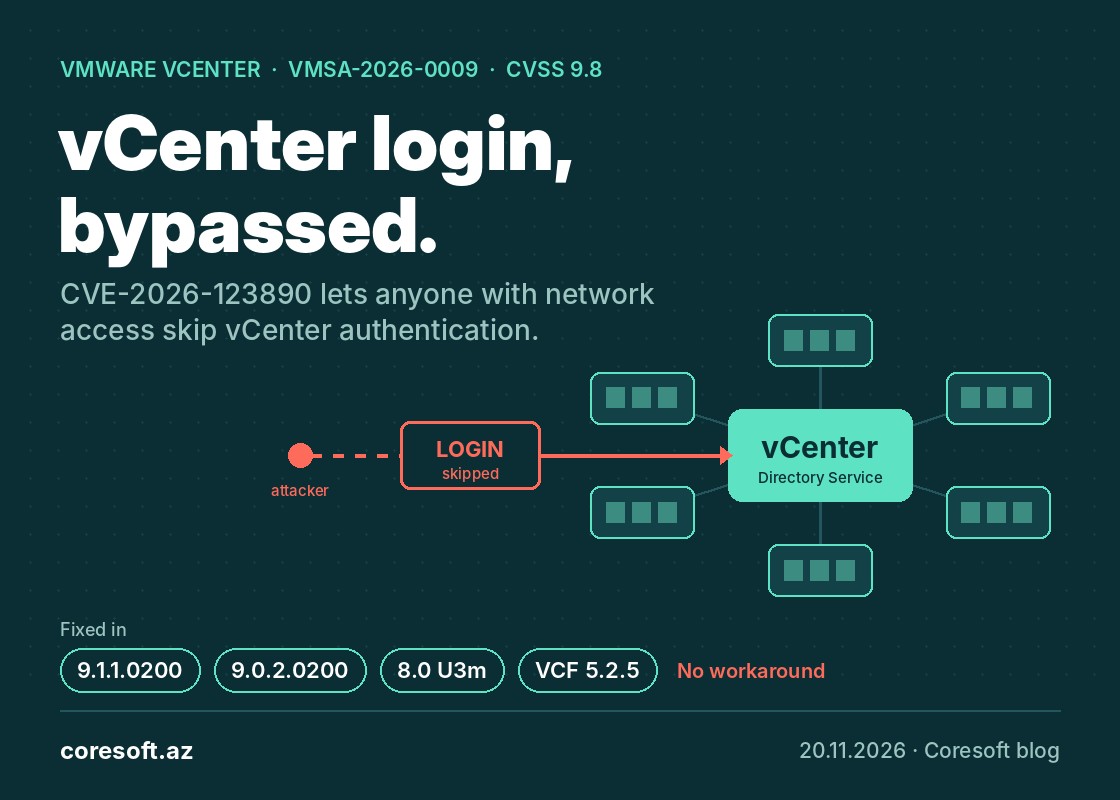
On 19 November Broadcom released a critical security update for VMware vCenter. The main flaw, CVE-2026-123890, carries a CVSS score of 9.8. It sits in vCenter's internal directory, the VMware Directory Service: an attacker with network access to vCenter can bypass authentication without knowing a password and without any user interaction. Mandiant reported the issue.
The weight of this becomes clear once you remember what vCenter does. Virtual servers, their disks and their networks are all managed from there, so whoever gets into vCenter sees the whole infrastructure. Affected are vCenter 8.0, 9.0 and 9.1, plus the builds shipped in Cloud Foundation 5.x and Telco Cloud. Whether you use Enhanced Linked Mode makes no difference.
The fixed versions are 9.1.1.0200, 9.0.2.0200 and 8.0 U3m. For VCF 5.x, Broadcom recommends applying vCenter 8.0 U3m through asynchronous patching and moving SDDC Manager to 5.2.5. There is no workaround, and these updates cannot be installed with Quick Patch. One catch: installing 8.0 U3m or 9.0.2.0200 blocks a planned upgrade to VCF 9.1.1. In that case either move vCenter to 9.1.1 first, or wait briefly for VCF 9.1.2.
vSphere 7.0 left general support in October 2025, and only customers with an extended support contract can get the fix. Versions 6.5 and 6.7 are not evaluated at all and should be treated as vulnerable. Broadcom has not reported any attacks so far, but one of the vCenter flaws disclosed this summer was being exploited within days. Until the update is done, limit access to vCenter to the management network: it reduces the risk, but it does not replace the update.
Sources: Broadcom VMSA-2026-0009, Broadcom Q&A, The Hacker News