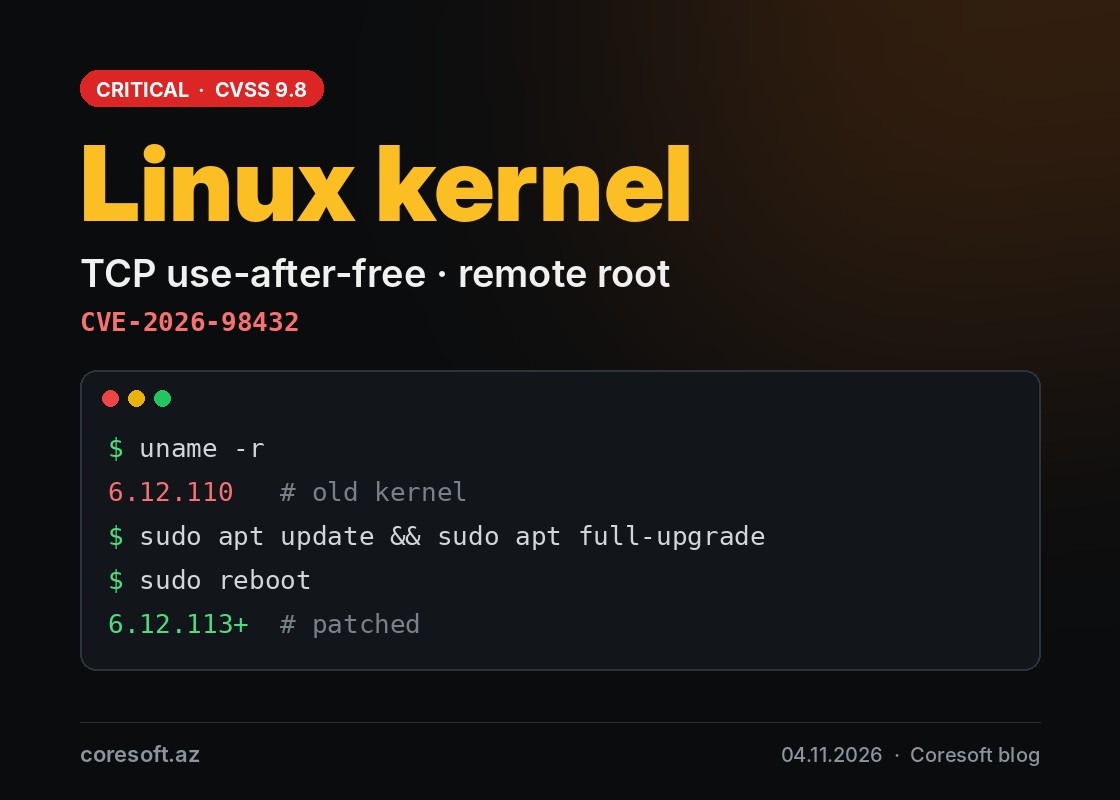
At the end of October a critical flaw was disclosed in the TCP code of the Linux kernel (CVE-2026-98432, CVSS 9.8). The problem is that memory is freed too early while a connection is being set up. Under the right conditions an attacker can read kernel memory, crash the server or, in the worst case, run commands as root.
The flaw was found by Anthropic researchers with the help of an AI model. In a lab, getting root on a server with a Multipath TCP (MPTCP) listener took less than an hour, with no password and no user interaction. There are no official reports of widespread attacks yet, but the technical details are already public.
The bug has been in every kernel since version 4.4, so it concerns almost every Linux server in use. Debian, SUSE, Oracle Linux and Amazon Linux have already shipped fixed packages, and other distributions are rolling out updates in stages.
What to do
- Check your distribution's security notice and install the kernel update. The new kernel only takes effect after a reboot, so verify the version with
uname -rafterwards. - If no update is available yet and you don't use MPTCP, turn it off with
net.mptcp.enabled=0. This lowers the risk but is not a full fix. - On cloud servers, use your provider's updated images.
The case also shows that AI is making the search for vulnerabilities much faster. That means the time it takes to install updates has to get shorter too.
Sources: CSO Online, Aikido.