ModSecurity is the most widely used open-source web application firewall (WAF) for Apache, nginx and IIS. Two security advisories the project published on GitHub came back into the news this week, and both matter to anyone running sites behind a WAF.
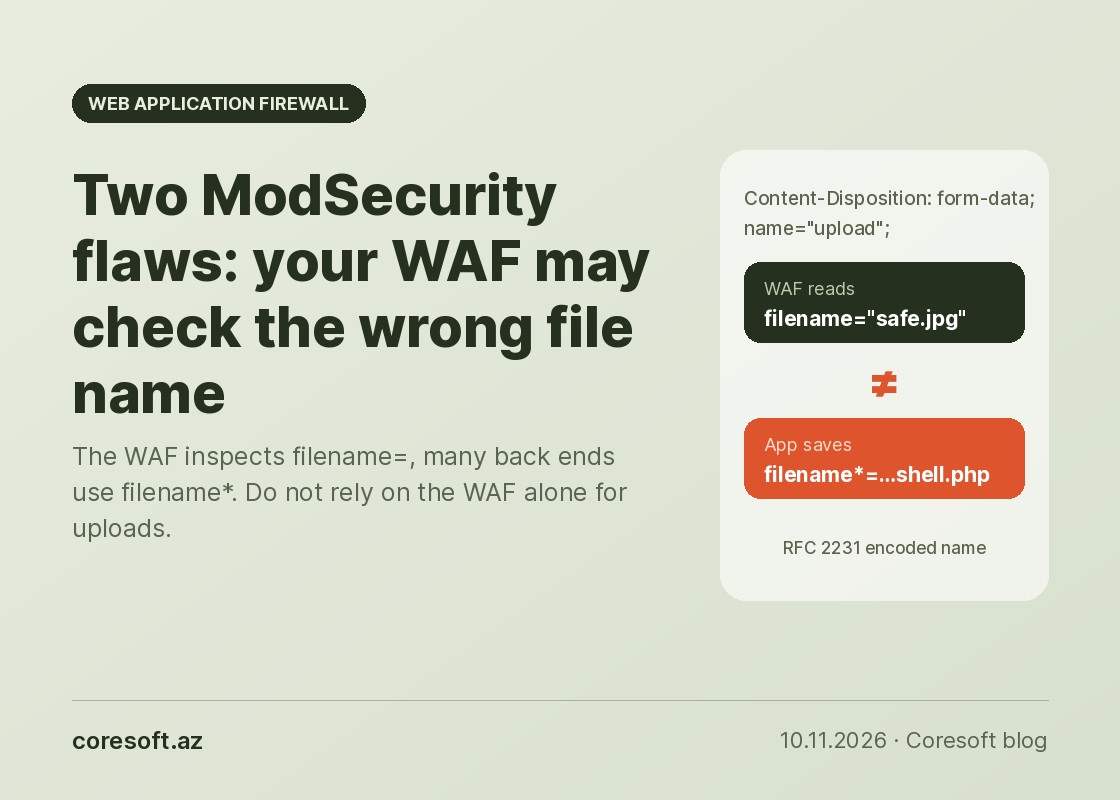
The first is about file uploads and is rated 8.6. In a multipart request a file name can be sent in two forms: the plain filename and the RFC 2231 encoded filename*. ModSecurity doesn't understand the second form, so the rules only check the first. Go, Python (Flask, FastAPI), Node.js (busboy, @fastify/multipart) and Java Spring prefer the encoded name. The result: the WAF sees "safe.jpg" while the application saves "shell.php". PHP's native upload handling is not affected. The official advisory does not list a fixed version yet.
The second is a memory bug in XML parsing in libmodsecurity 3.0.15 and 3.0.16 (CVE-2026-73857, CVSS 7.5). A single unauthenticated request can crash a worker process and in some cases may lead to code execution. It is only reachable when SecParseXmlIntoArgs is On or OnlyArgs; the default is Off. The advisory lists 3.0.17 as the fixed version, and ModSecurity v2 is not affected.
Check which ModSecurity version your server actually loads and make sure SecParseXmlIntoArgs is Off. For uploads, don't rely on the WAF alone: ignore the name the client sends, save files under a name you generate, block executable extensions and keep uploads outside the web root.
Sources: GitHub: filename*, GitHub: CVE-2026-73857, Cyber Security News.