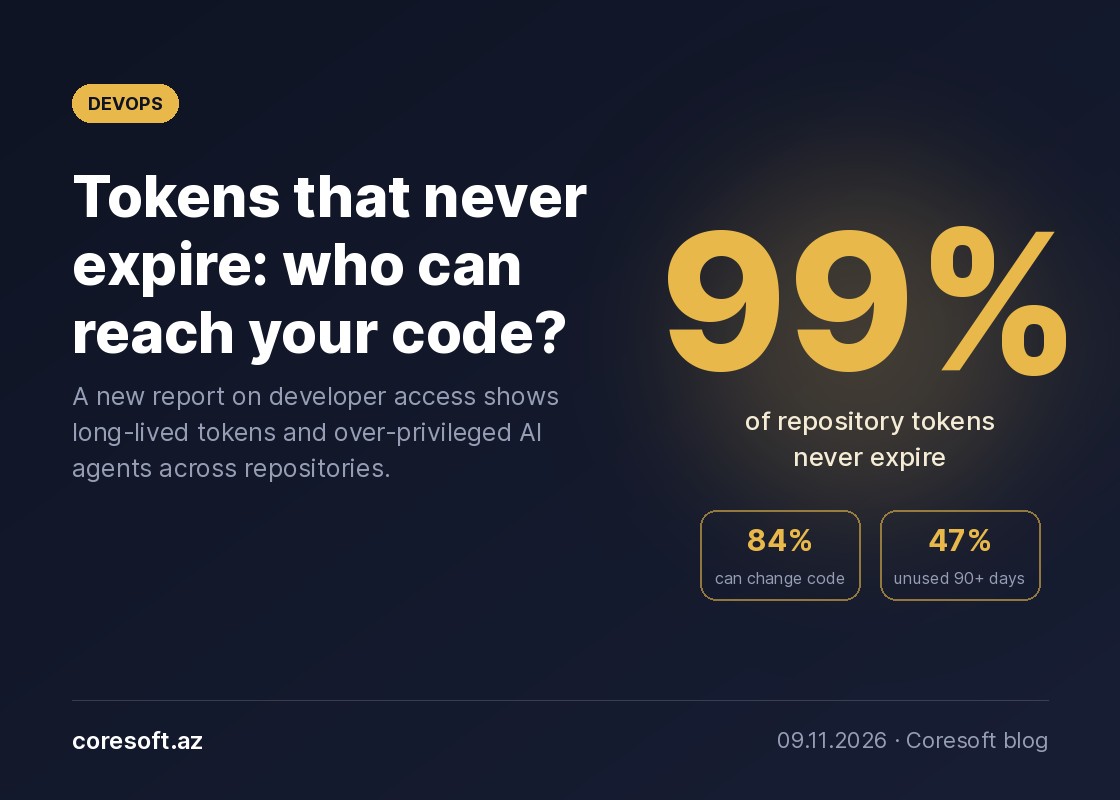
In early November BlueFlag Security published "The State of Developer Risk 2026". The report draws on data about tens of thousands of identities and tokens at the company's customers and puts numbers on a problem development teams often overlook. 99% of repository access tokens have no expiry date, 84% allow code changes, and 47% have gone unused for more than 90 days without being revoked.
A token like that can sit in a forgotten script, an old CI setting or the laptop of someone who has left the company. One leaked token lets an attacker read the code, slip in a malicious change and move from there into the software supply chain.
The figures on AI tools stand out too. 68% of the identities agents run under have administrator rights, 81% work without behavioural monitoring, and unapproved agents were found in 83% of organisations. In 40% of repositories the main branch is unprotected, and in 56% of organisations code was merged despite failed checks.
Fixing this doesn't take a big project. Give every token an expiry date and the least access it needs, and revoke the ones unused for 90 days. In CI/CD, move from long-lived keys to short-lived access such as OIDC. Protect main branches and don't let administrators skip code review either. Give AI agents their own limited accounts, and once a quarter review who can reach what.
Sources: Help Net Security, SiliconANGLE.