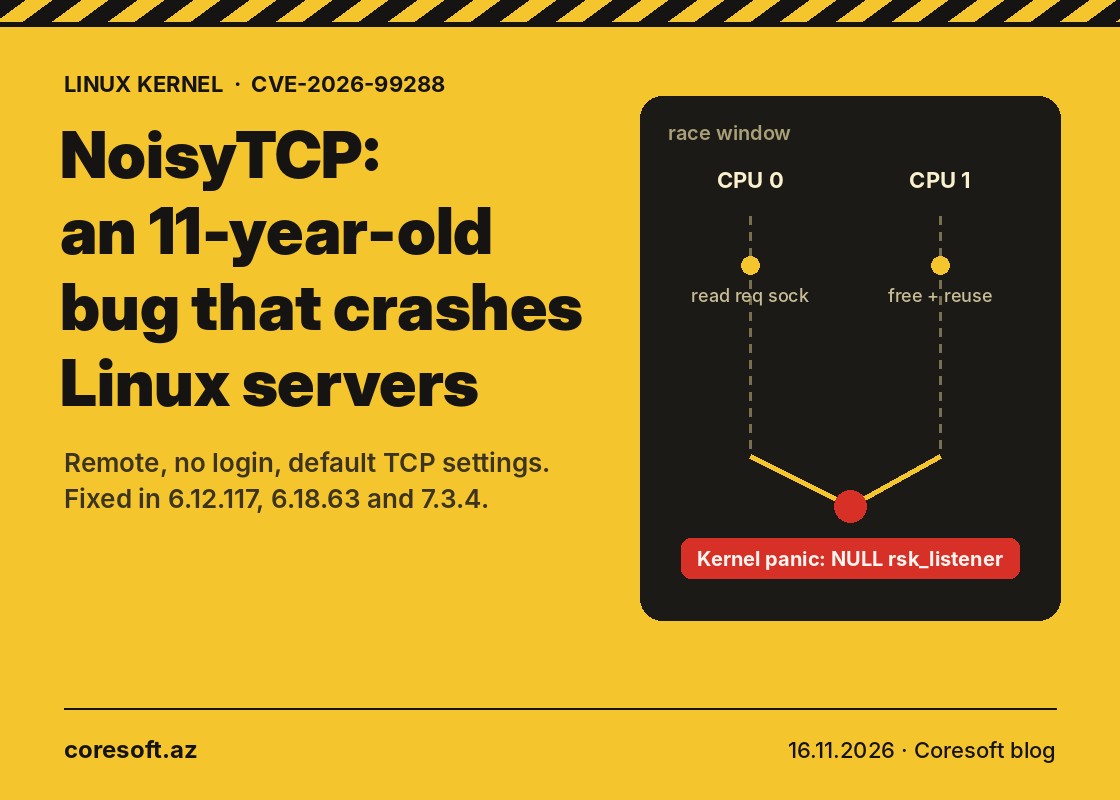
On 15 November researcher Hyunwoo Kim disclosed a flaw that has been sitting in the Linux kernel's TCP code since 2015. Named NoisyTCP and tracked as CVE-2026-99288, it needs no password and no special configuration: a server with an internet-facing TCP port (web server, SSH, mail) can be crashed with traffic sent from outside. Red Hat rates it 7.5 out of 10.
The cause is a race condition around SYN cookies. While one CPU core reads the record of a half-open connection, another has already freed that memory and reused it, so the kernel follows a null pointer and panics. In Kim's tests, default Nginx, Apache and SSH setups on virtual machines went down within 5 seconds to 2 minutes. A crash inside a container takes the whole host with it. Remote code execution has not been shown so far.
The fix is in stable kernels 6.12.117, 6.18.63 and 7.3.4. Updated packages are already out for Debian 12 and 13, while Ubuntu, RHEL, AlmaLinux and Rocky had no fix as of 16 November. Once your vendor ships one, install the new kernel and reboot.
Until then there are two stopgaps. The first is turning SYN cookies off with net.ipv4.tcp_syncookies=0; it has to be set in every container's network namespace, and it weakens protection against SYN floods. The second is running the external interface with a single RX queue and RPS and RFS disabled. Either way, try the change on a test server first. To see where you stand, check your kernel with uname -r and keep an eye on your distribution's security advisories.
Sources: iTnews, ComputingForGeeks, FOSS Linux.