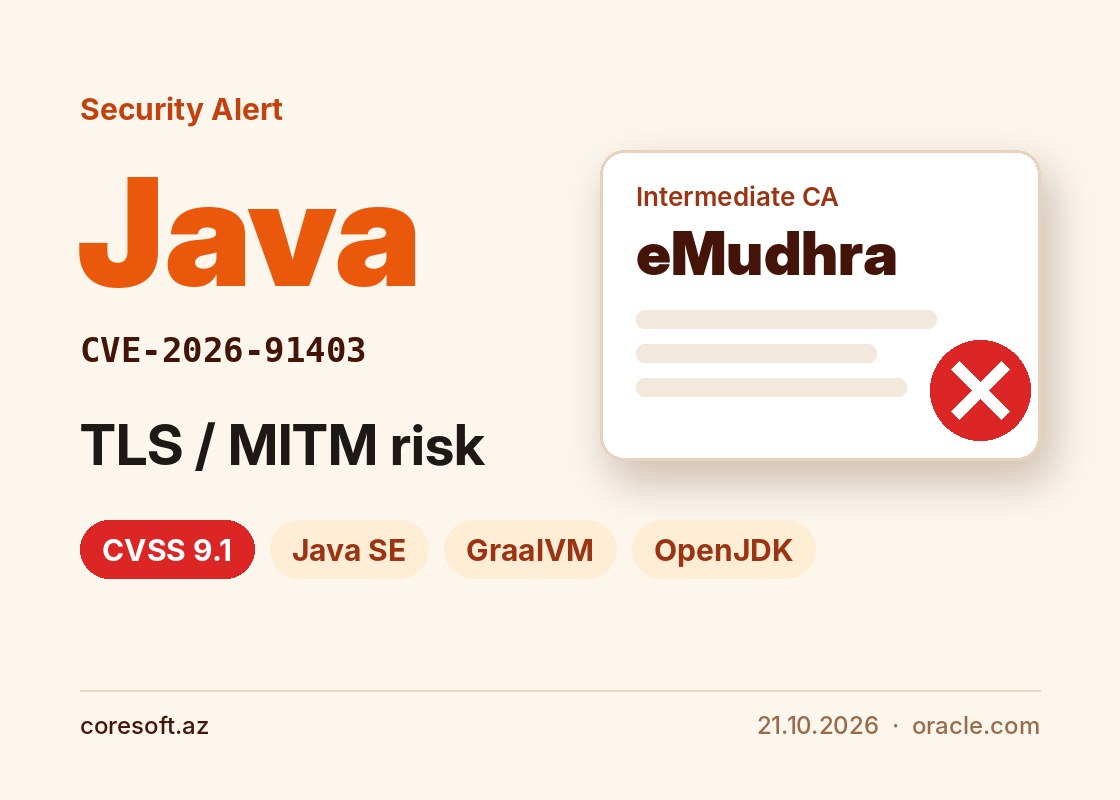
On 21 October Oracle published an out-of-band Security Alert. The flaw, CVE-2026-91403, affects Java SE and GraalVM and has a CVSS score of 9.1, which makes it critical.
This time it is not about running code on a server. The problem is that Java still trusted compromised intermediate CA certificates belonging to eMudhra. A fake certificate made with one of them could look genuine to a Java application. An attacker could then step into the TLS connection between the application and a server and read or change the data being sent (a MITM attack).
The issue exists in both Oracle Java and OpenJDK. Affected versions include the Java 8, 11, 17, 21, 25 and 27 lines as well as GraalVM. Node.js blocked the same certificates in its 21 October release.
What to do
- Update Java, or the OpenJDK distribution you use, to the latest release.
- If you can't update right away, the certificates can be blocked temporarily with the
blocked.certsfile. Instructions are in the Oracle and OpenJDK advisories. - Also check the Java version inside Java-based products and Docker images, since they often ship with their own Java.