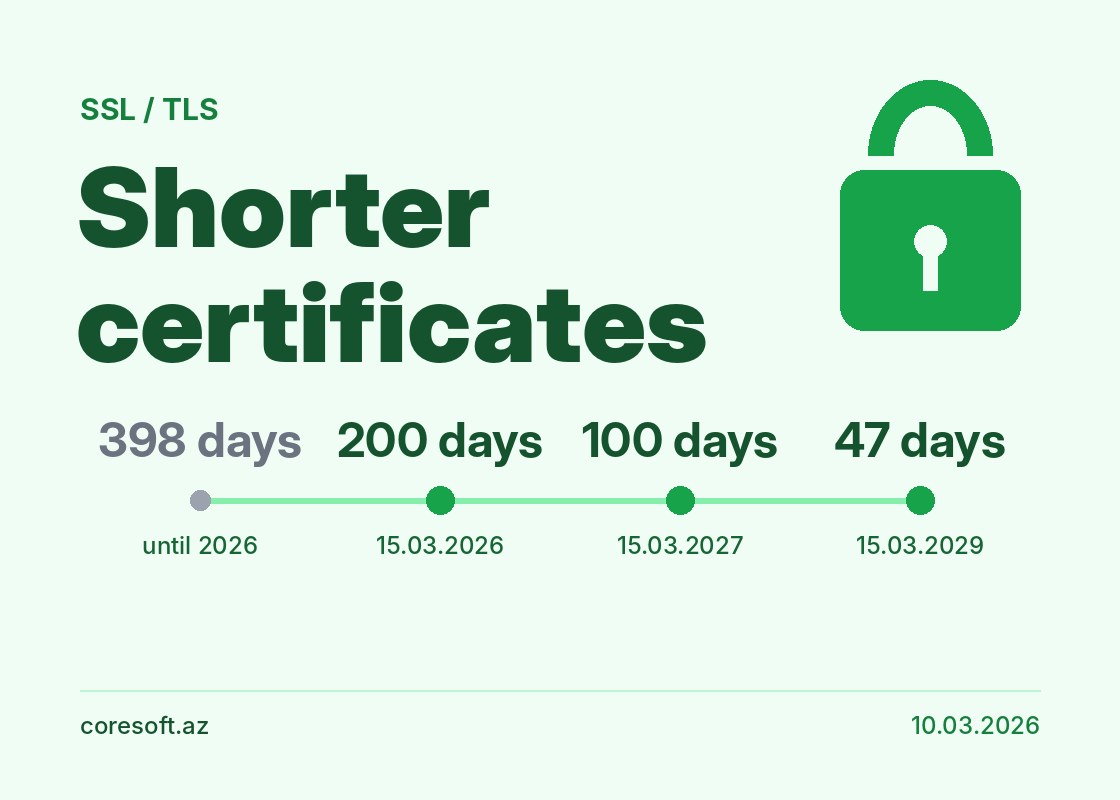
The CA/Browser Forum, which brings together browser makers and certificate authorities, has decided to cut the maximum validity of SSL/TLS certificates in stages. The first step comes on 15 March 2026.
The schedule
- 15 March 2026: at most 200 days (until now 398 days).
- 15 March 2027: 100 days.
- 15 March 2029: 47 days.
Certificates issued before each date keep their original lifetime; the change only applies to new ones.
Why they are getting shorter
The shorter a certificate lives, the less room there is to misuse a stolen or wrongly issued one. Domain ownership is also checked more often.
What site owners should do
Anyone renewing certificates by hand will have a lot more work: 47 days means a renewal roughly every month. The reliable answer is automation. Services like Let's Encrypt and ACME tools such as certbot and acme.sh renew certificates on time by themselves. Even with automation in place, it is wise to have an alert that watches the expiry date.
Source: DNSimple.