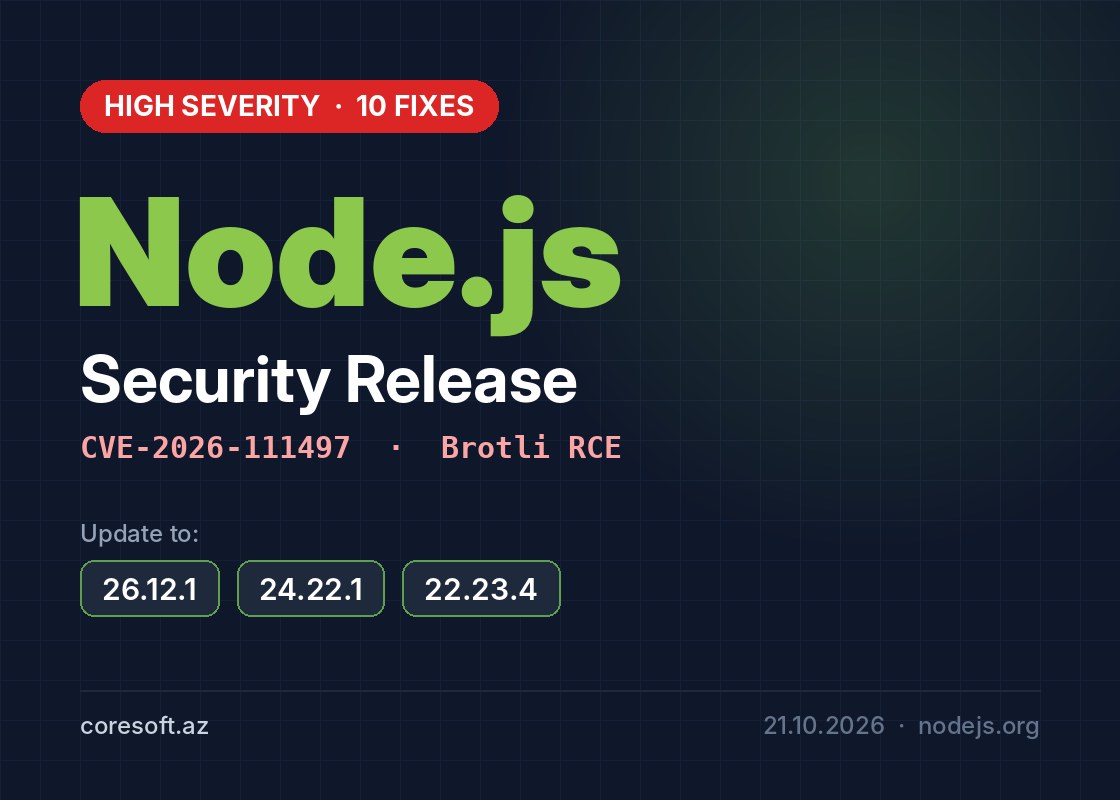
On 21 October, the same day as the PHP2Shell flaws in PHP, the Node.js team shipped a security release of its own. It fixes 10 vulnerabilities, 4 of them rated high.
The most serious one is in the Brotli decoder bundled with Node.js (CVE-2026-111497). Specially crafted compressed data can corrupt the process memory. That can crash the server, leak data from memory or, in the worst case, let outside code run on the server.
Brotli is a compression format used widely by browsers and servers. If your application decompresses Brotli data it doesn't control, for example a request body or a response from another service, with node:zlib, this flaw applies to you.
The other flaws
The other three high-severity issues are in how TLS certificates and DNS names are checked. For example, an oddly written IP address such as 0127.0.0.1, or a domain name containing a NUL character, could fool the check. This matters most for systems that send requests to addresses supplied by users, such as webhooks and integrations. The release also closes vulnerabilities in the bundled OpenSSL, c-ares and Undici libraries.
What to do
- Update Node.js to 26.12.1, 24.22.1 or 22.23.4. There is no workaround for these flaws, so updating is the only fix. You can check the version on a server with
node -v. - If you use Docker, the official
nodeimages were updated on 21 October, but running containers need to be rebuilt. - If your project depends on the
undicipackage directly, update it to the latest version as well. - Node.js 20 and older, as well as 21, 23 and 25, are no longer supported and will not get a fix. If you are on one of them, don't put off the upgrade any longer.
Support from Coresoft
The Coresoft team checks the versions used in Node.js and PHP projects, updates them safely and tests that applications keep working after the update. To use this service, contact us.
Sources: nodejs.org, Konfirmity.